
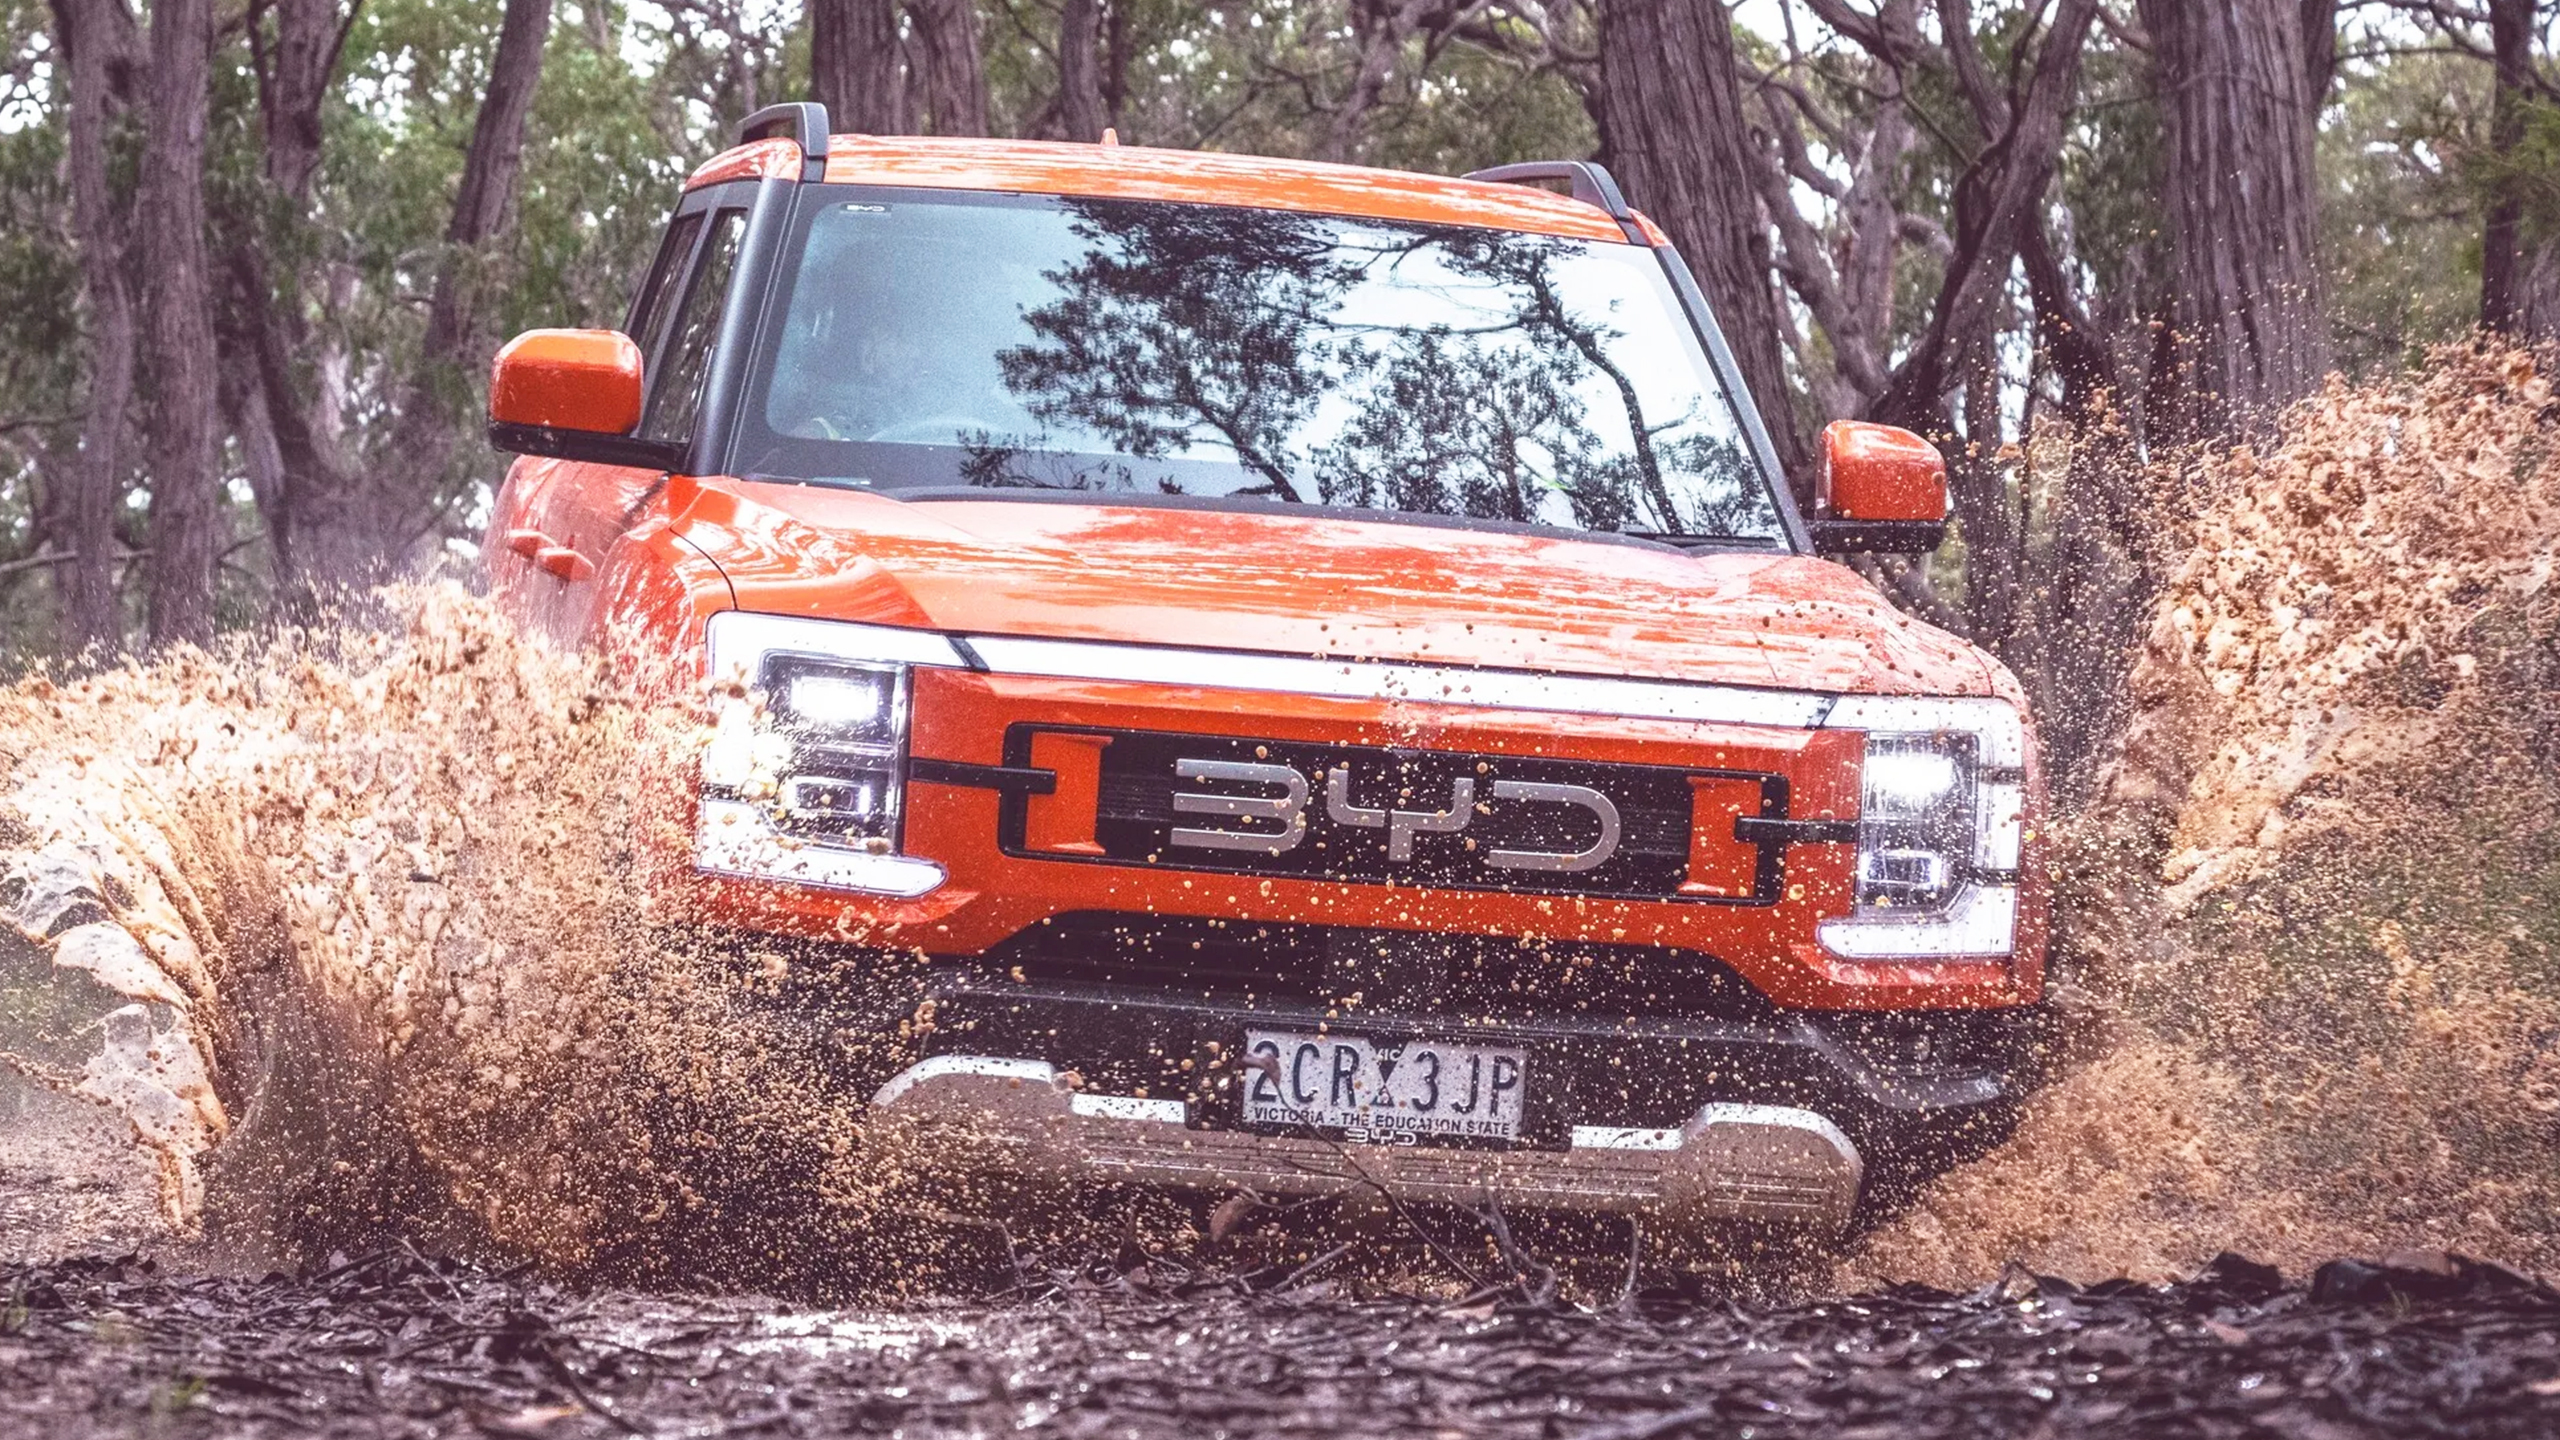

BYD is in damage control mode after an Australian television documentary showed a cybersecurity expert taking over key functions of its Shark 6 pickup truck, including its microphones, door locks, and headlights. The Chinese automaker’s response has been swift, detailed, and clearly designed to reframe the narrative.
The ABC’s Four Corners program gave cybersecurity researcher Dan Hreszczuk two weeks with a Shark 6. He managed to listen through the cabin microphones, manipulate the audio system, and lock and unlock the doors. The most dramatic footage showed him remotely killing the headlights while the truck was being driven at night, then flipping on the windshield wipers for good measure.
BYD says it has figured out how Hreszczuk got in. He breached the Android Debug Bridge using a specialized tool and loaded an unauthorized third-party application onto the infotainment system. BYD replicated the exploit internally and confirmed the vulnerability exists, but added a caveat the documentary left out: accessing location data and the microphone requires the driver to accept a permission prompt on screen.
That’s an important detail, if it’s true. A permission pop-up is a speed bump, not a wall, but it does change the threat calculus.
BYD says it’s developing an over-the-air update that will disable the pathway used to enable the ADB, which is normally turned off. No timeline was given. If other models share the vulnerability, they’ll get patched too.
The headlights and wipers are a different story entirely, and this is where BYD’s counterattack gets sharper. The automaker says those functions were not compromised through software alone. Hreszczuk physically spliced into the Shark 6’s wiring harness and connected a low-cost Raspberry Pi computer to the vehicle’s internal CAN bus. That requires hands-on access underneath the vehicle, not a laptop in a parking lot across the street.
Hreszczuk confirmed the physical access in a blog post. He also acknowledged the same technique would work on plenty of other modern vehicles. CAN bus vulnerabilities are not unique to BYD. They’re an industry-wide problem that security researchers have been warning about for years.
BYD has responded by adding physical isolation and device authentication requirements to the OBD interface. That should make it harder for anyone plugging unauthorized hardware into the diagnostic port.
The documentary clearly rattled BYD at a sensitive moment. The Shark 6 has been selling well in Australia, and the brand is trying to establish credibility in a market that already views Chinese automakers with some skepticism. A prime-time exposé showing a hacked BYD driving blind through the dark is not helpful marketing.
But the Four Corners program also appears to have conflated two very different types of vulnerabilities. Software exploits through the infotainment system are a legitimate remote threat. Physically tapping into a vehicle’s wiring harness is something else entirely, closer to hot-wiring than hacking, and applicable to virtually every car on the road.
That distinction matters, and the documentary’s failure to draw it clearly does a disservice to viewers trying to assess actual risk. Every modern connected vehicle carries cybersecurity exposure. Singling out BYD without that context feels less like journalism and more like theater.
BYD has not said when the OTA patch will arrive. Australian owners are waiting.
Share this Story